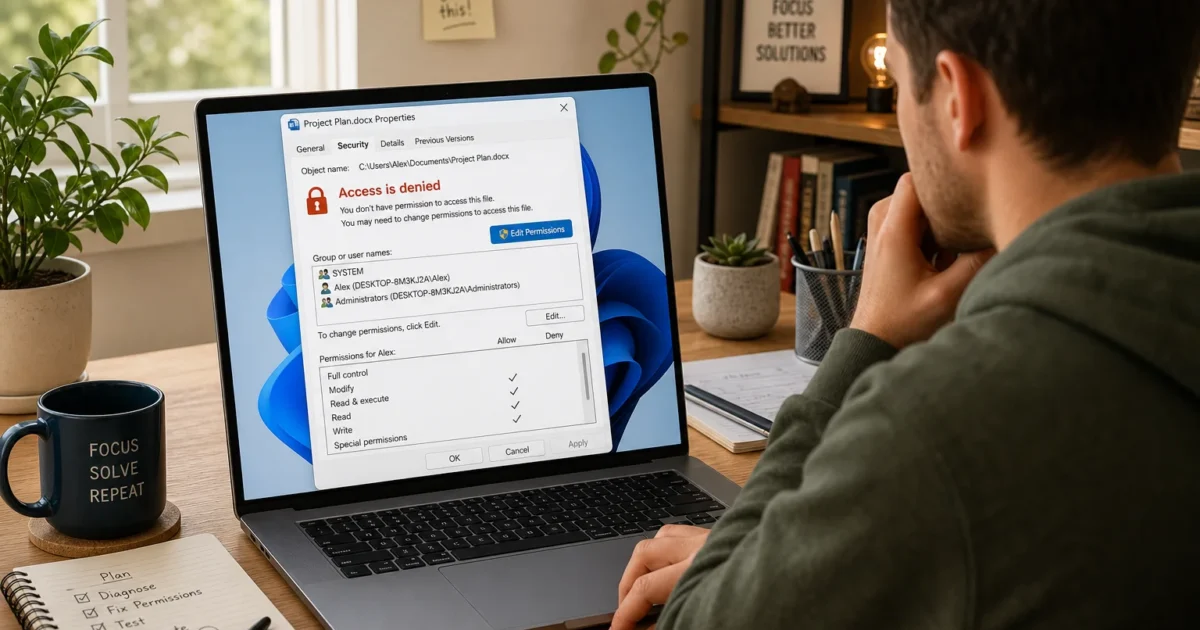
If you’re getting “Access is denied” on a folder, or you want to prevent other users on your PC from opening specific files, NTFS permissions control both, and you can edit them from any file’s Properties dialog. These steps apply to Windows 10 and Windows 11, including version 24H2.
Understanding Windows File and Folder Permissions
Every file and folder on an NTFS-formatted Windows drive carries an access control list (ACL): a list of users and groups, each with specific permissions either allowed or denied. Windows checks that list every time someone tries to open, edit, or delete the item.
The six standard permissions are:
| Permission | What it controls |
|---|---|
| Full Control | Read, write, modify, delete, change permissions, and take ownership |
| Modify | Read, write, and delete, but not change permissions or ownership |
| Read & Execute | Open and run files |
| List Folder Contents | See what’s inside a folder (folders only) |
| Read | Open files without editing them |
| Write | Create and save files |
Deny overrides Allow. If a user has Full Control granted directly but belongs to a group that’s denied Full Control, the Deny wins every time.
Permissions inherit by default. A folder passes its permissions down to everything inside it. That’s why checkboxes in the Security tab are often greyed out: the permission is flowing from a parent folder, not set directly on the item you’re viewing.
One important limitation: Permissions keep casual users out, but any local administrator on the PC can take ownership of a file or folder and grant themselves whatever access they want. For genuine privacy, encrypt your hard drive or use tools like VeraCrypt. Permissions and encryption layer well together.
Cloud files are a separate situation. If your files are in OneDrive or SharePoint, the Security tab won’t control who can access them online. Cloud sharing is managed through the OneDrive or SharePoint interface. NTFS permissions only govern access on this device and on local network shares.
How to View and Change Permissions
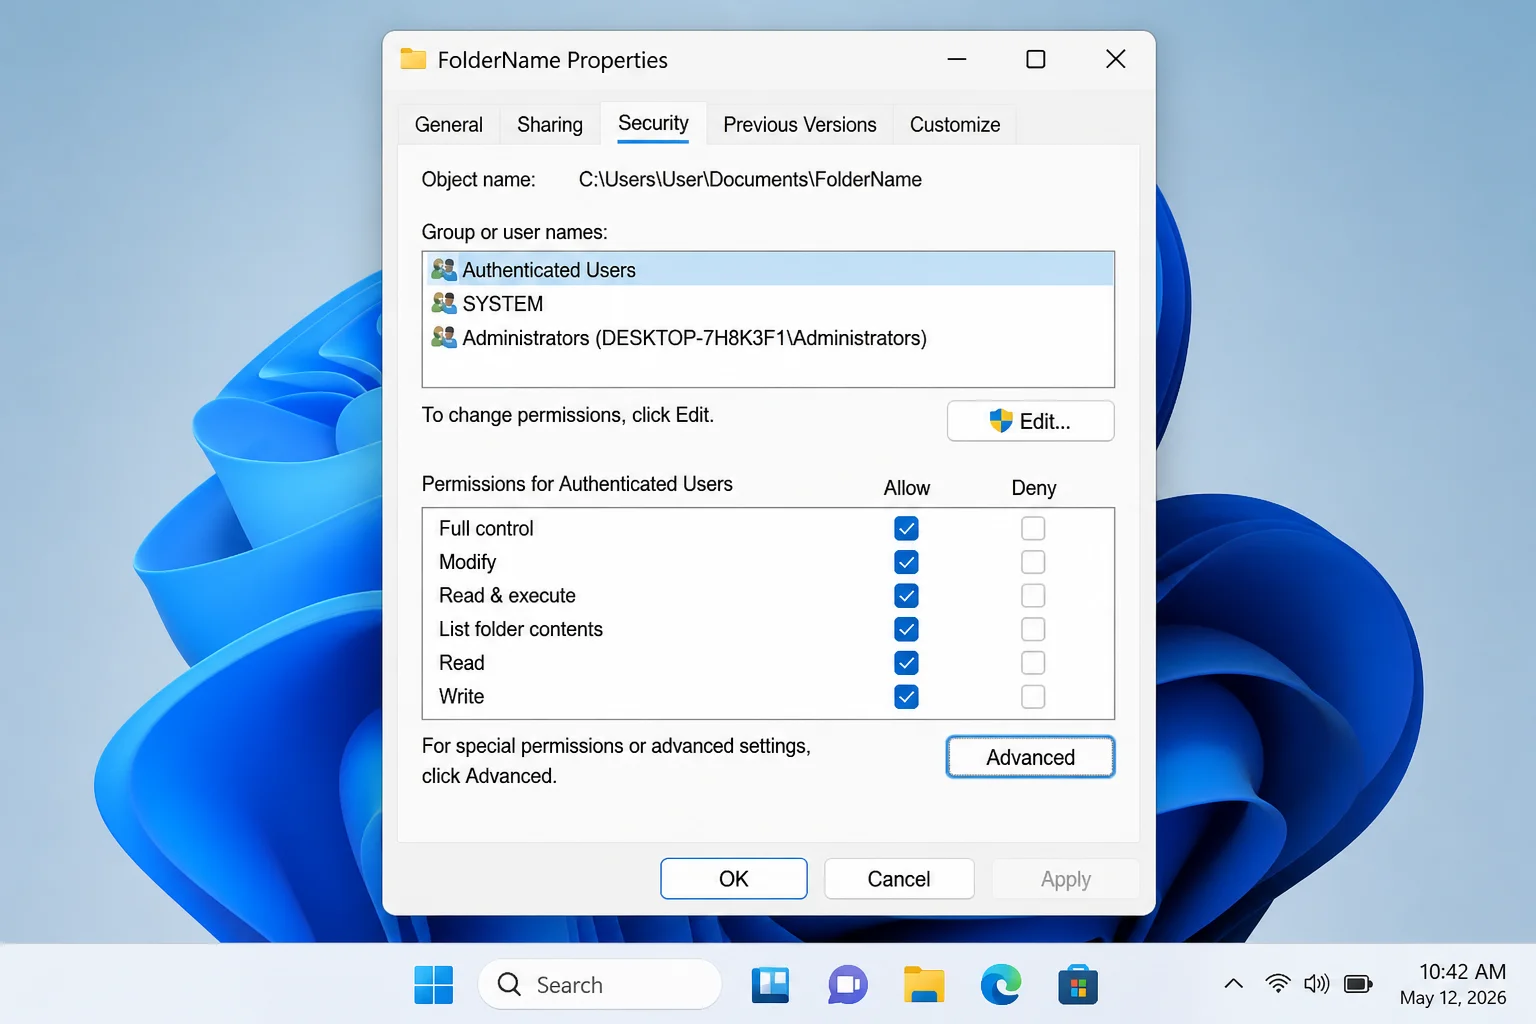
Open the Security tab
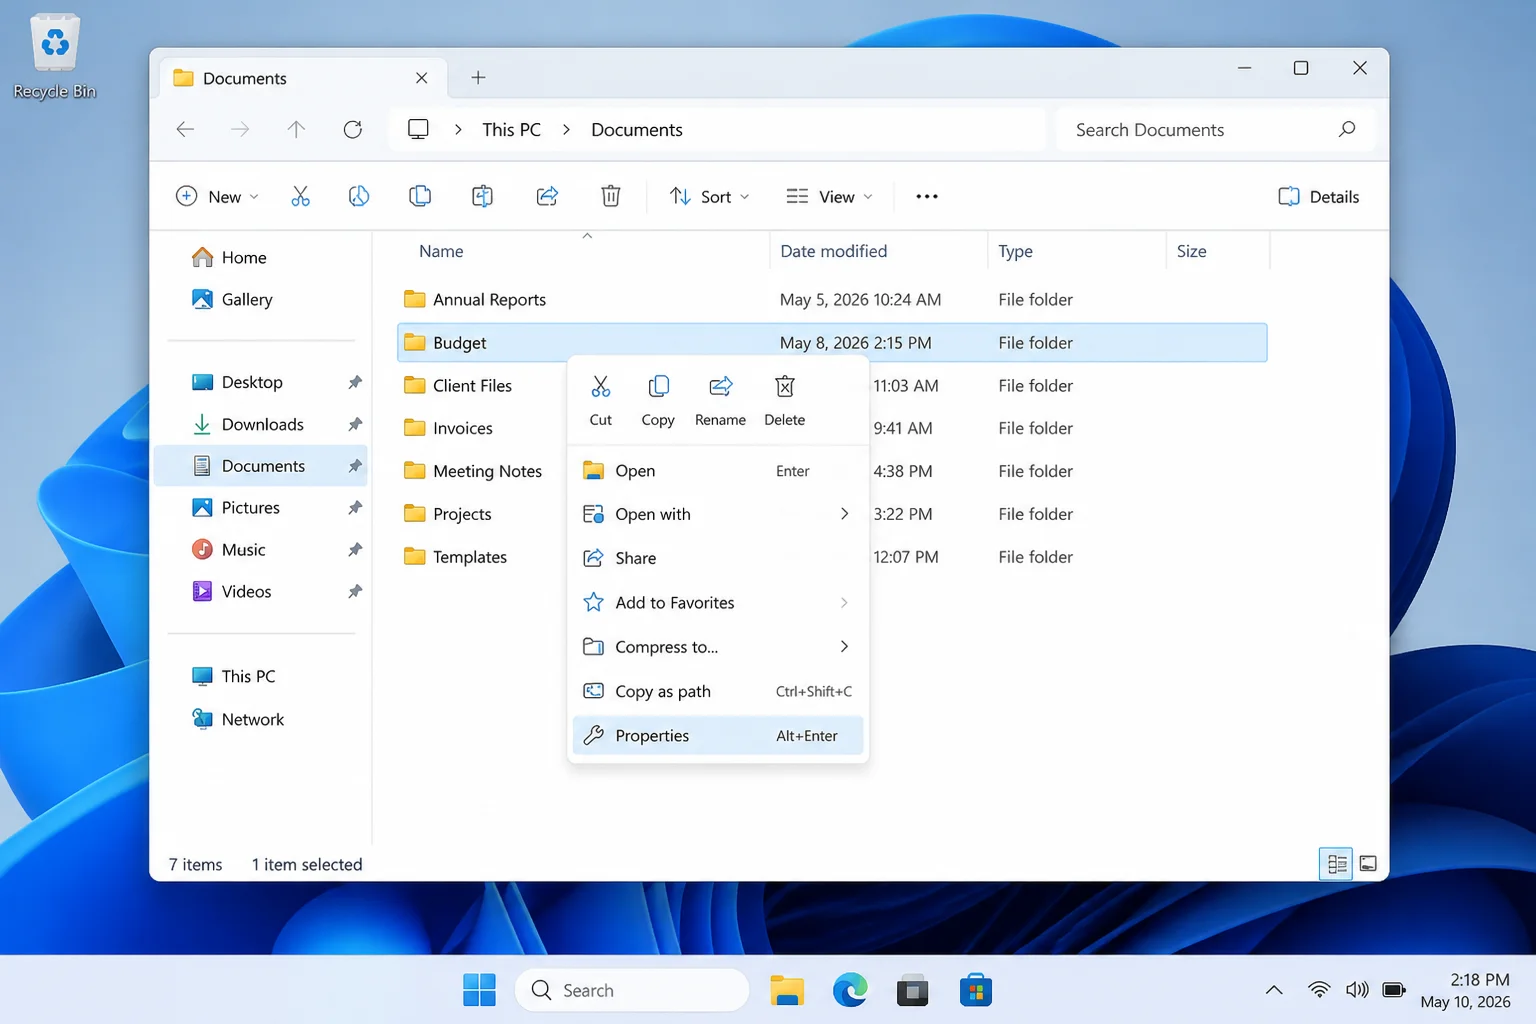
- In File Explorer, right-click the file or folder.
- Select Properties.
- Click the Security tab.
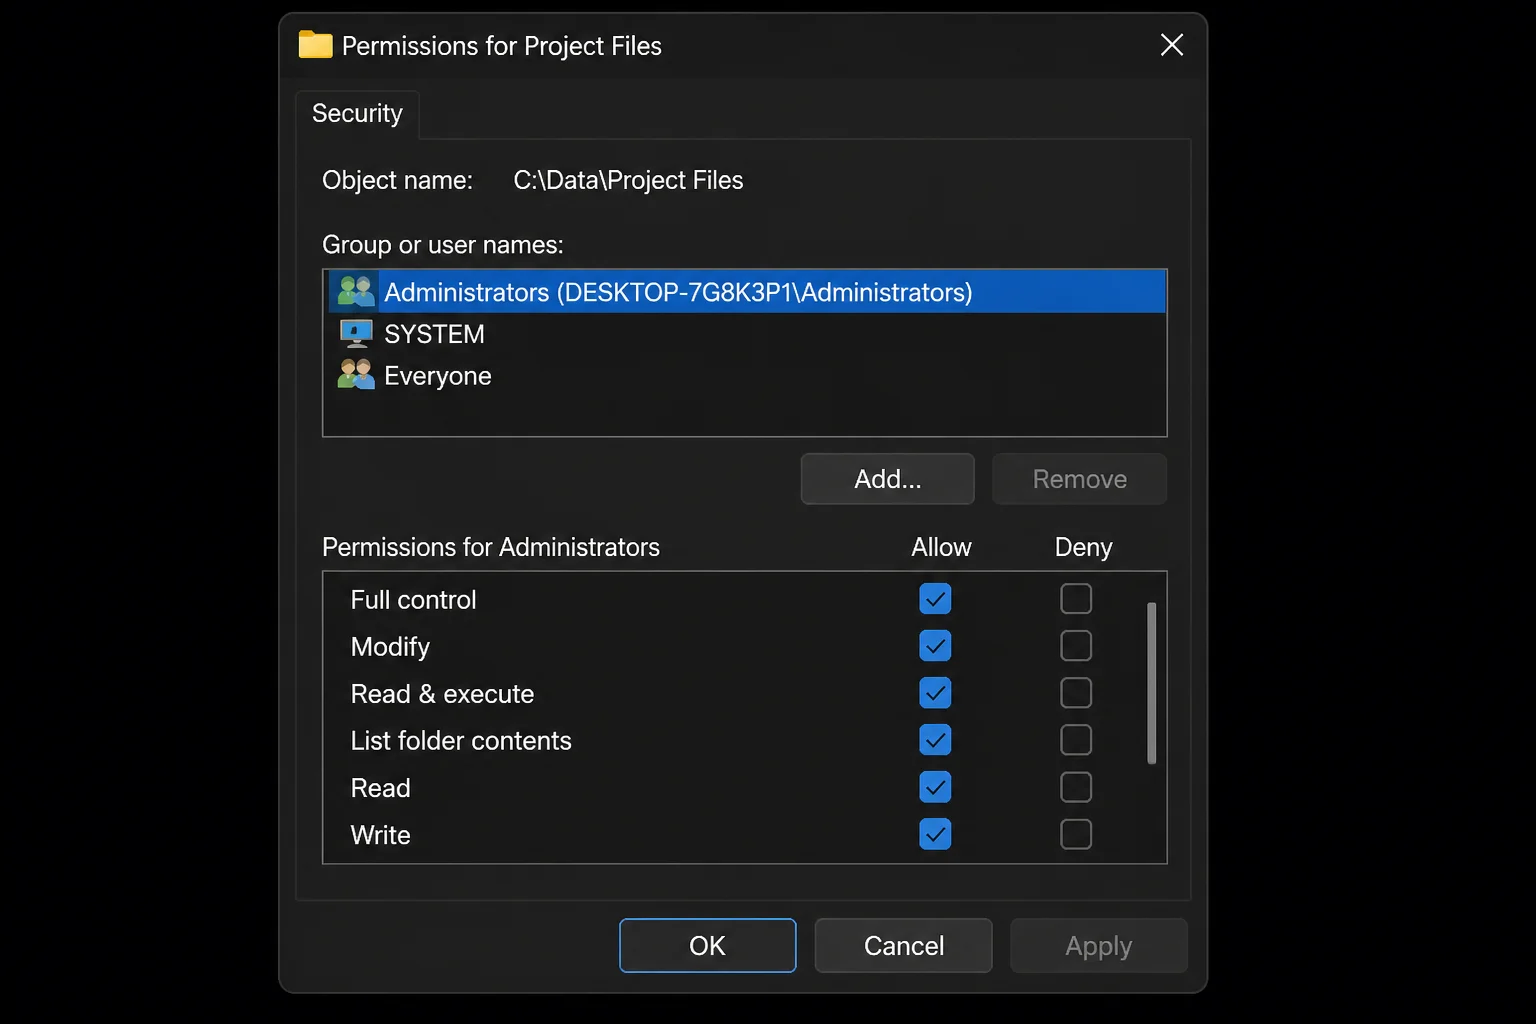
The Group or user names panel lists every account with an entry on this item. Click any name to see its current permissions in the panel below.
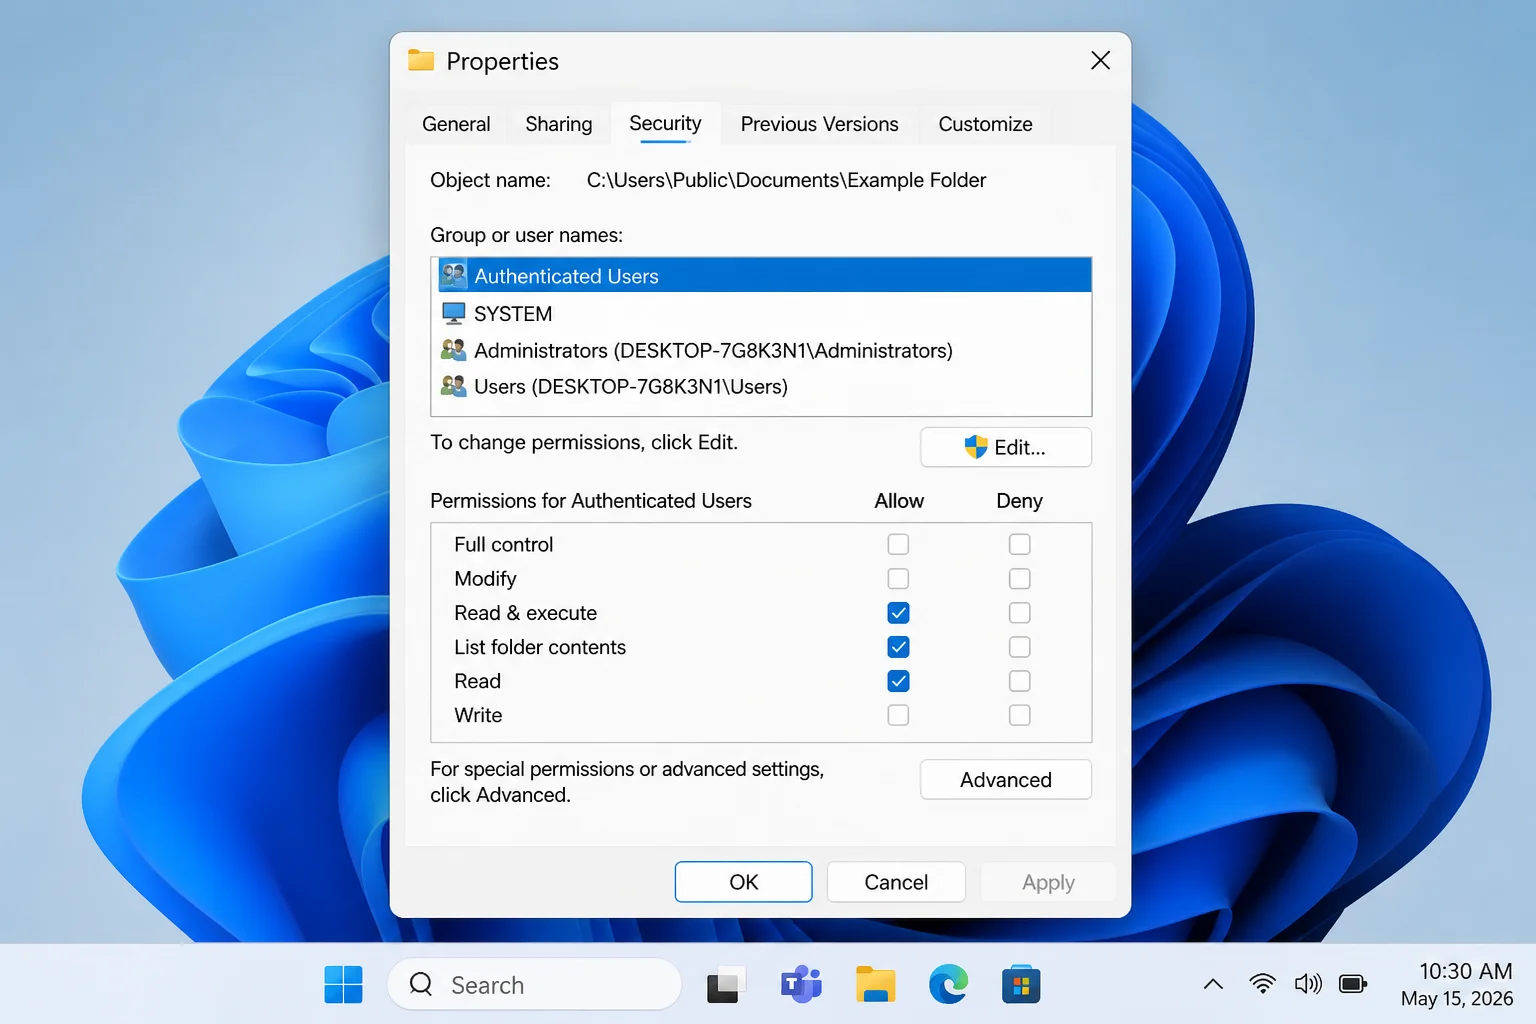
Edit permissions for an existing user or group
- On the Security tab, click the user or group you want to change.
- Click Edit.
- In the Permissions for [name] dialog, check or uncheck the Allow or Deny boxes.
- Click Apply, then OK.
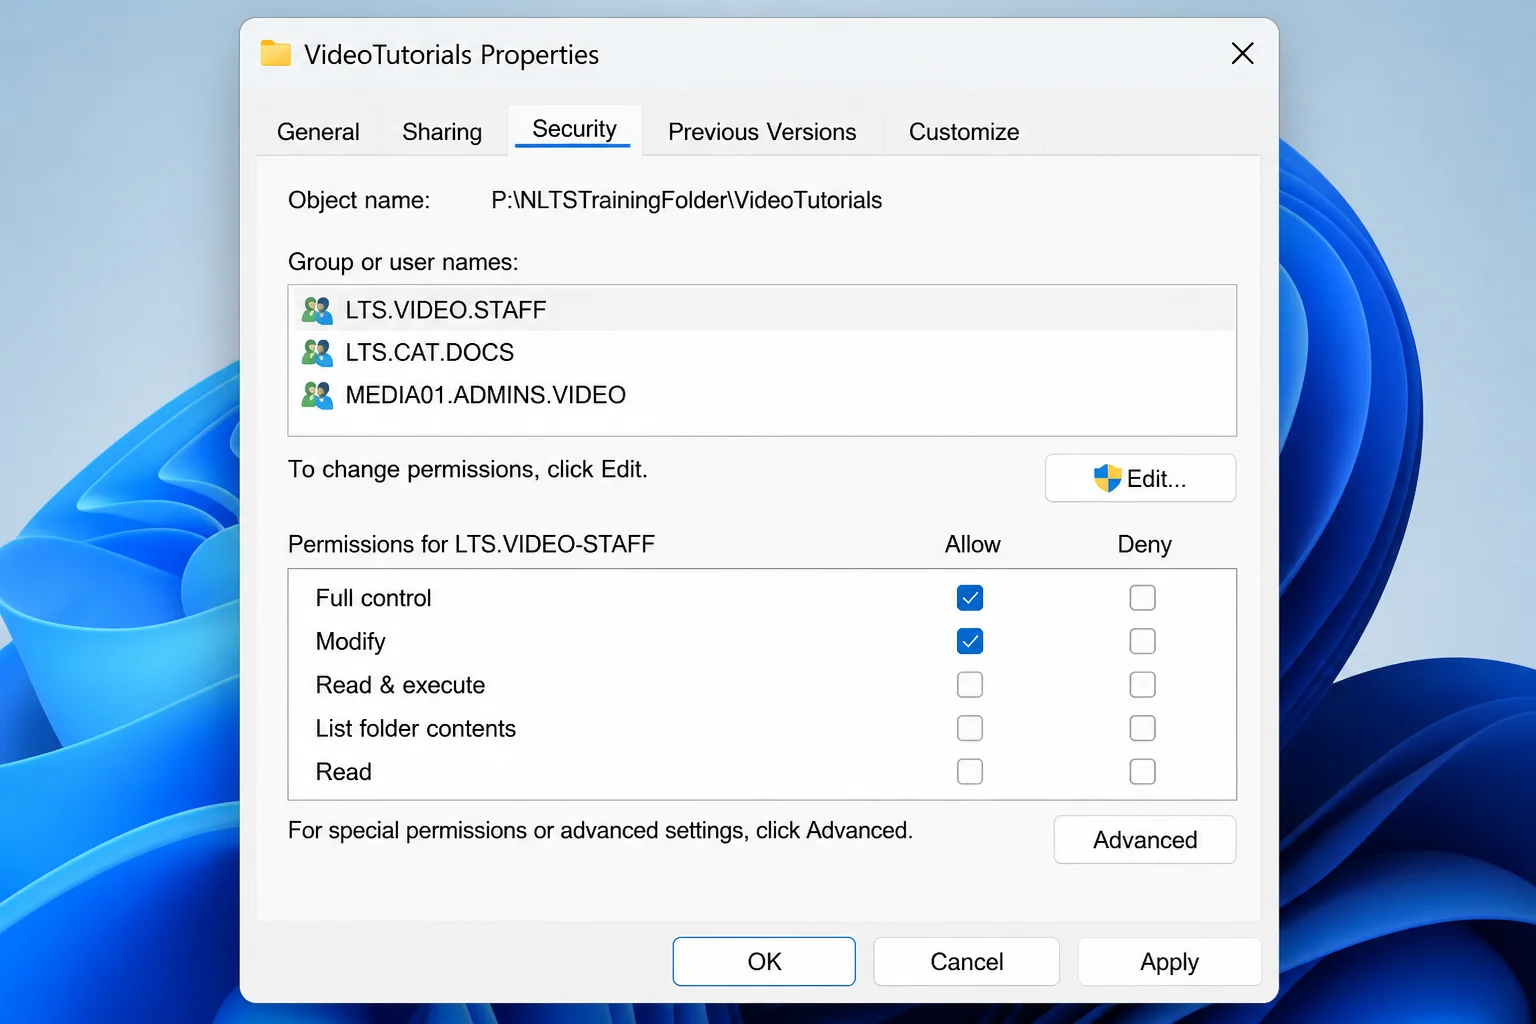
If the checkboxes are greyed out, the permissions are inherited from a parent folder. You’ll need to disable inheritance before you can edit them. See the section below.
How to Add or Remove a User or Group
Add a user or group
- On the Security tab, click Edit.
- Click Add.
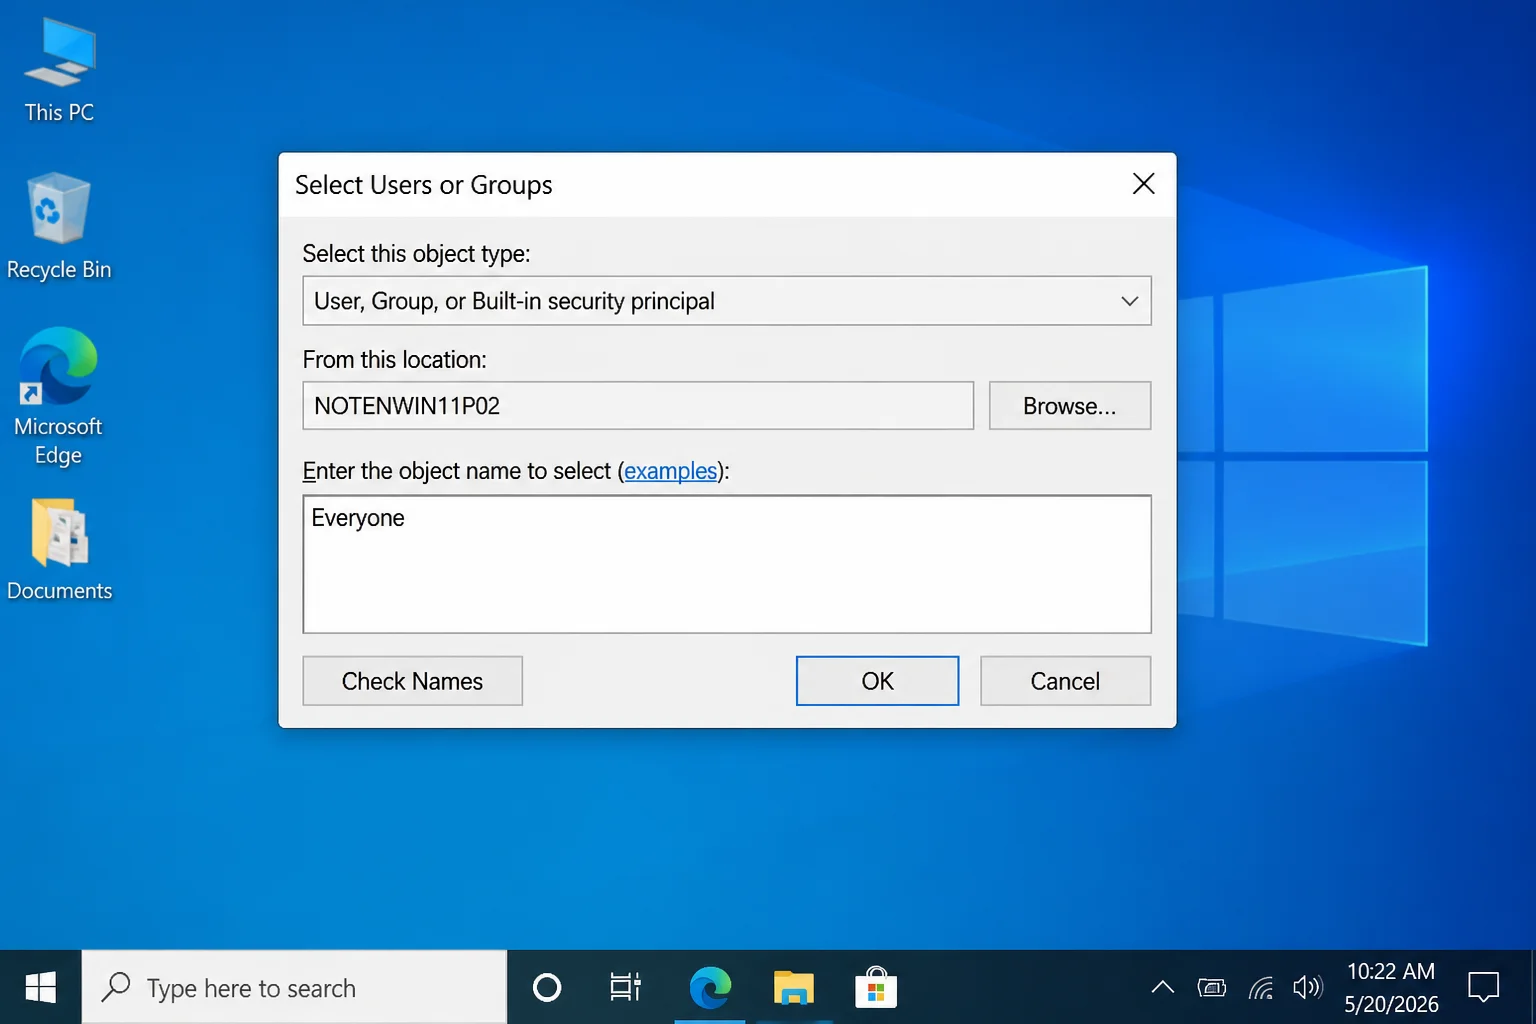
- In the Enter the object names to select field, type the username or group name.
- Click Check Names to confirm it resolves correctly.
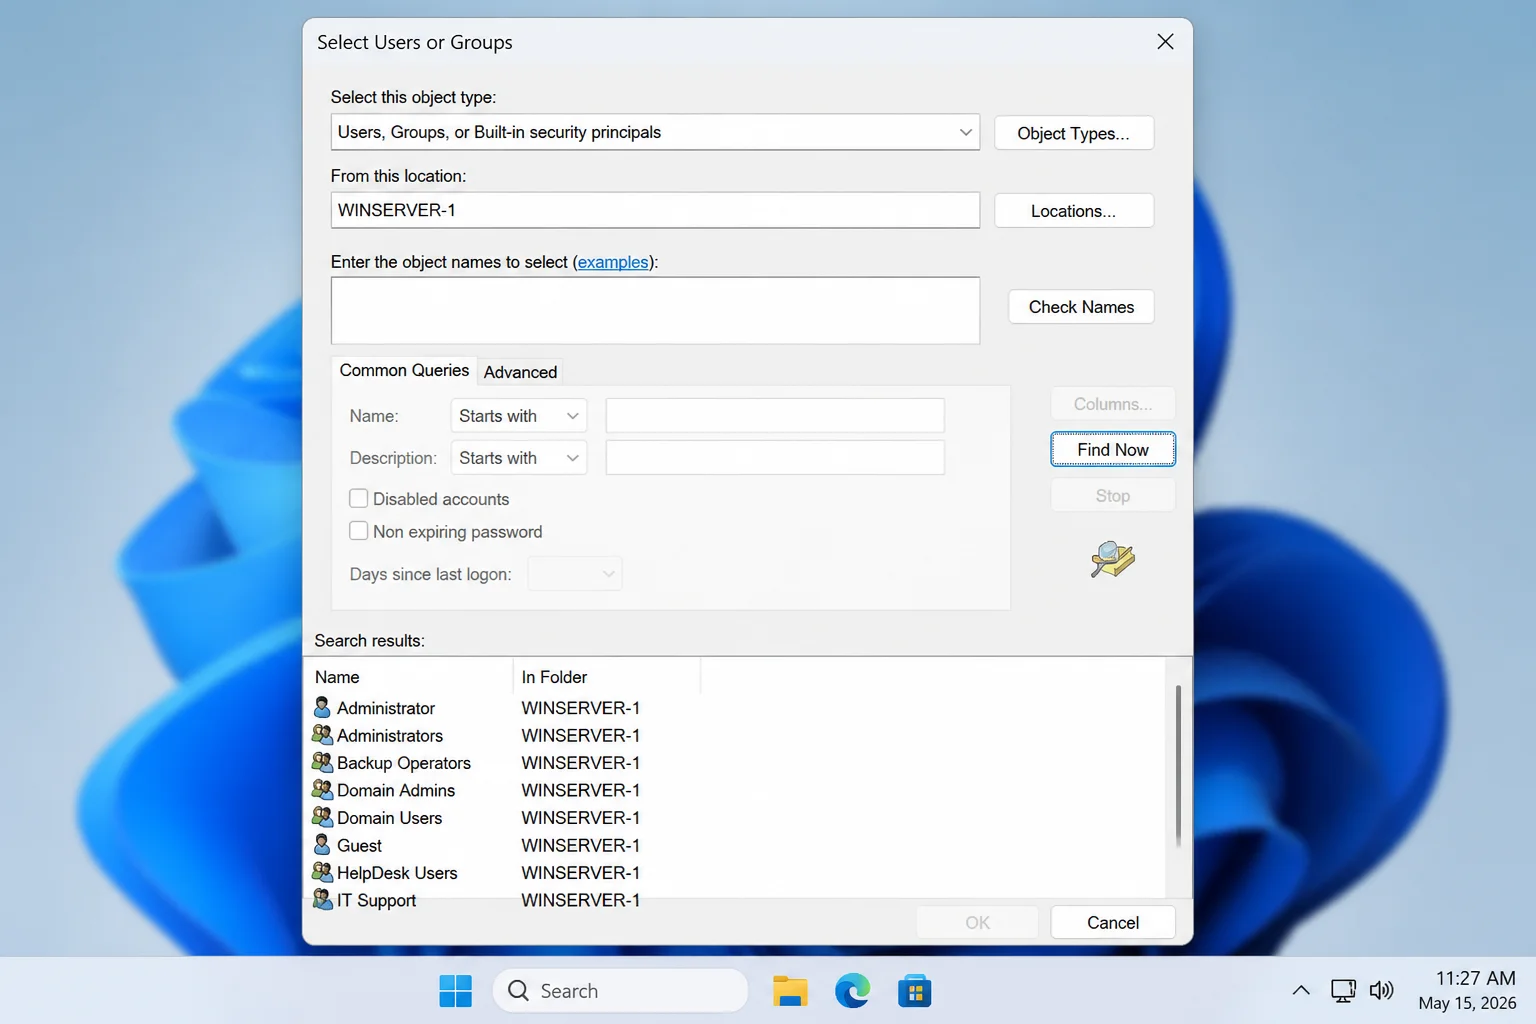
- If you don’t know the exact name, click Advanced, then Find Now to browse every local user and group.
- Click OK to add the account to the list.
- Select the new entry and set its Allow or Deny permissions.
- Click Apply, then OK.
Use Deny sparingly. Applying it to a group blocks every member, even accounts that have an explicit Allow entry elsewhere.
Remove a user or group
- On the Security tab, click Edit.
- Select the user or group you want to remove.
- Click Remove, then Apply, then OK.
Remove is greyed out for inherited entries. Disable inheritance first, then come back and try again.
How to Disable Inheritance
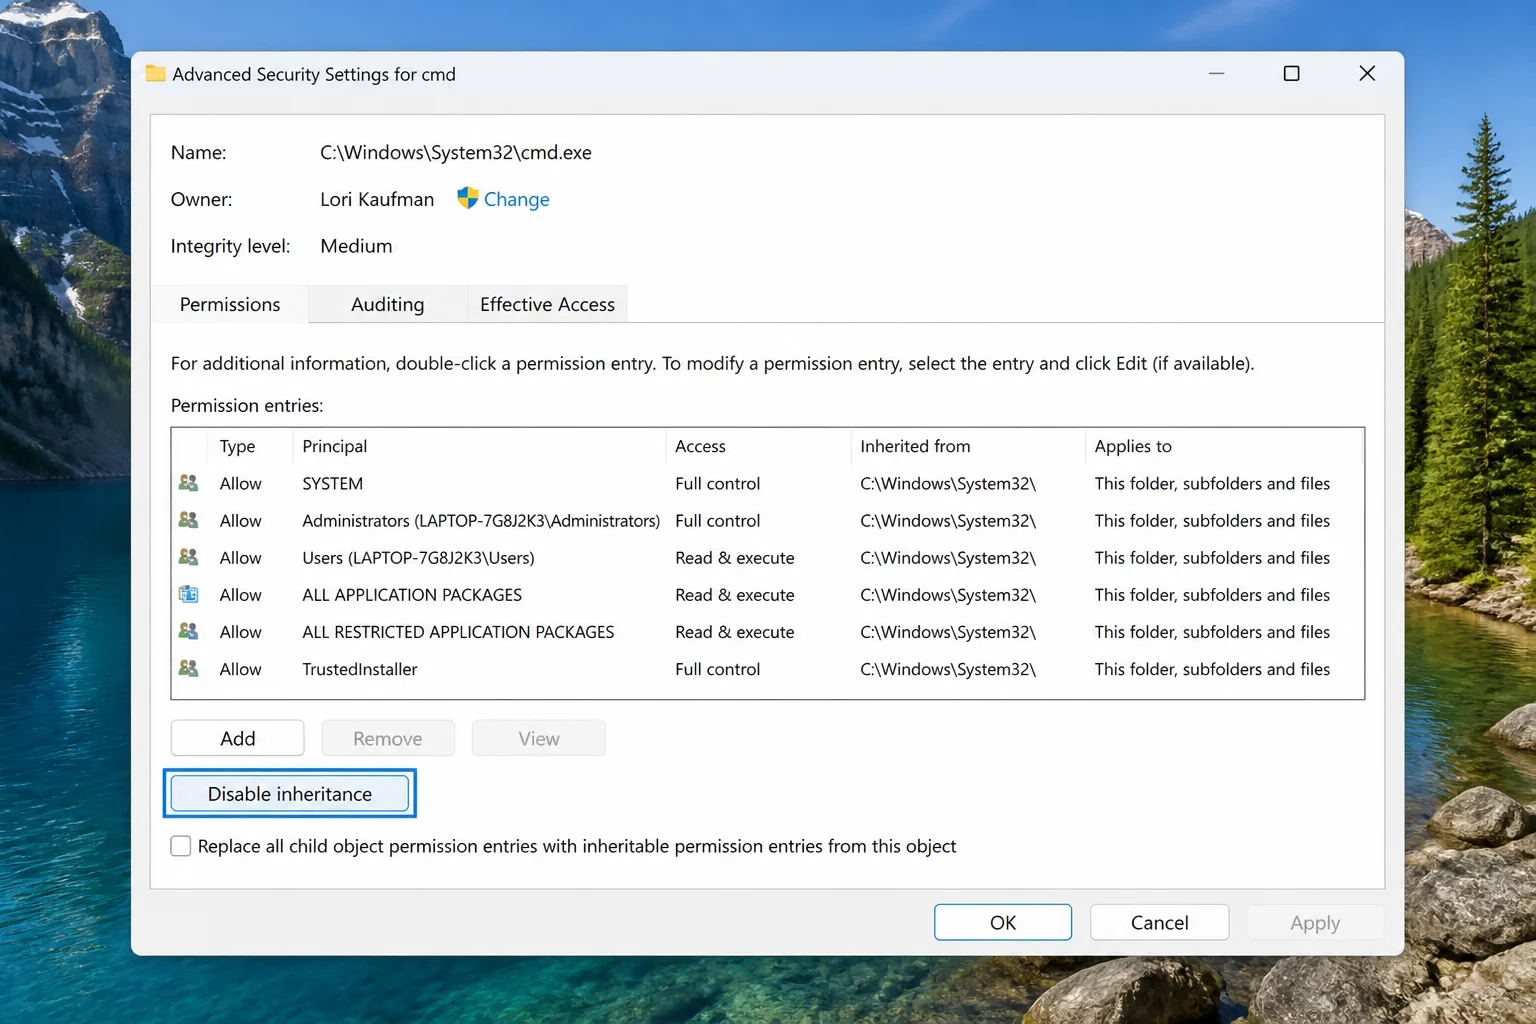
Disabling inheritance cuts the link to the parent folder, so your custom permissions won’t be overwritten from above.
- Right-click the folder, select Properties, then click the Security tab.
- Click Advanced.
- In the Advanced Security Settings dialog, click Disable inheritance.
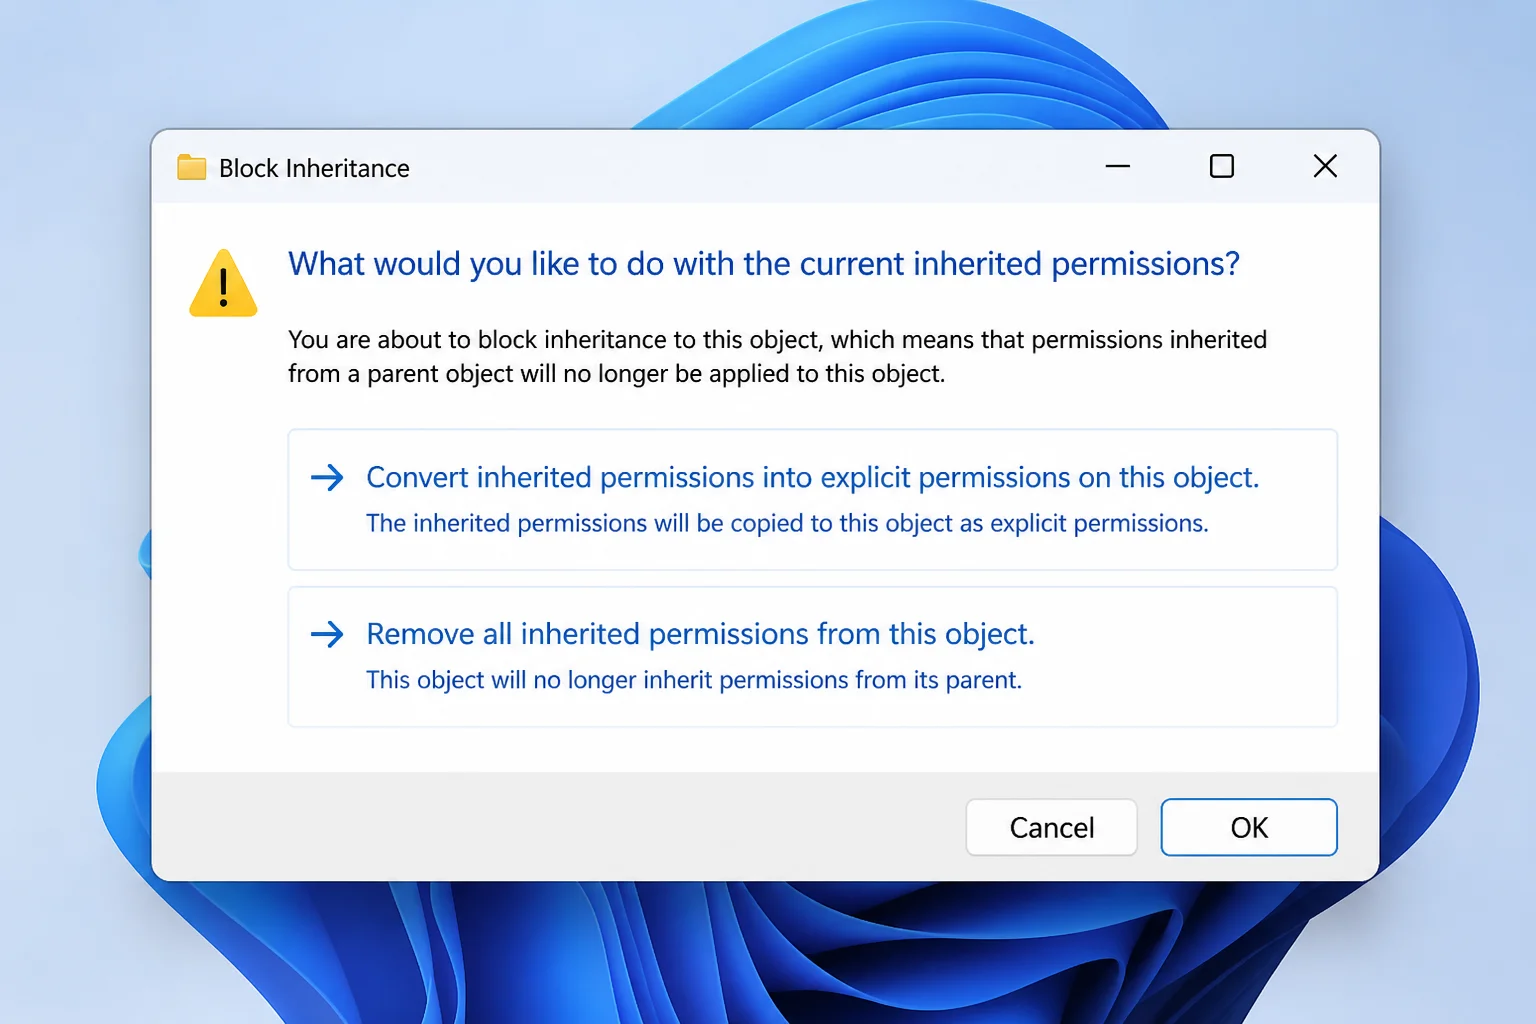
- A dialog asks what to do with the existing inherited entries. Choose one:
– Convert inherited permissions into explicit permissions on this object: keeps everything as-is but makes every entry editable. Pick this if you’re not sure. – Remove all inherited permissions from this object: clears the list entirely. Only choose this if you’re building permissions from scratch.
- Click Apply, then OK.
Every entry is now editable. Nothing will be greyed out.
How to Take Ownership of a File or Folder
If the permissions dialog itself is locked, or you’re hitting “Access is denied” even with admin rights, the file is probably owned by a system account like TrustedInstaller. Taking ownership puts you in control.
- Right-click the file or folder, select Properties, then click the Security tab.
- Click Advanced.
- At the top of the Advanced Security Settings dialog, click Change next to the current owner name.
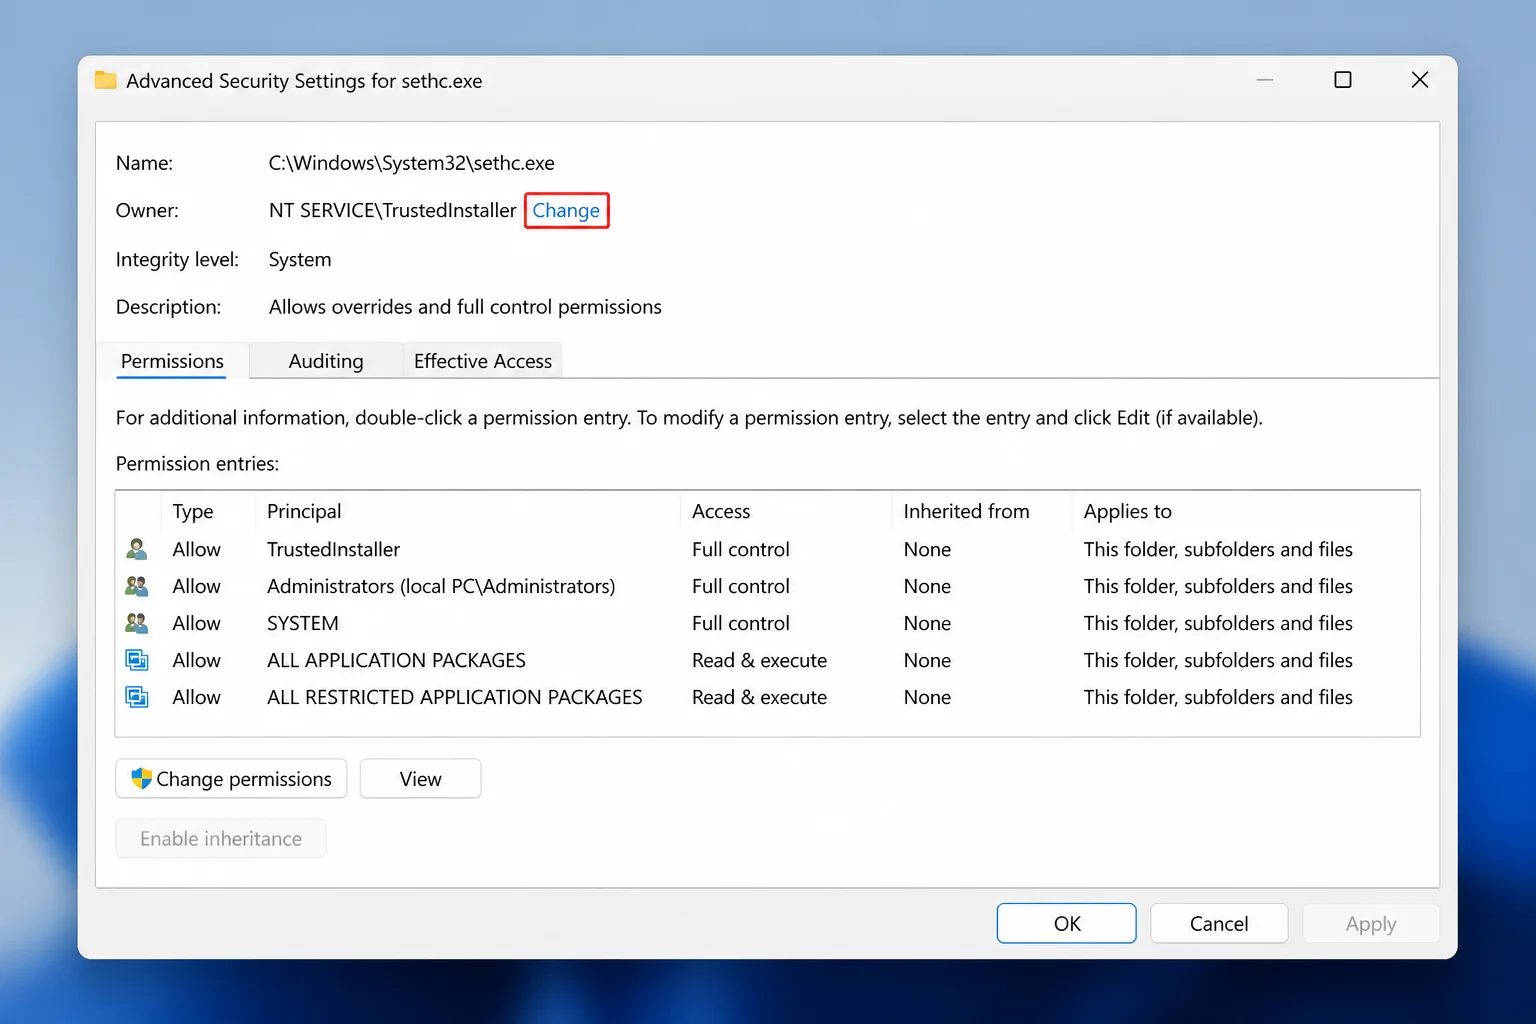
- Type your username, click Check Names, then OK.
- To extend ownership to every subfolder and file inside, check Replace owner on subcontainers and objects.
- Click Apply, then OK.
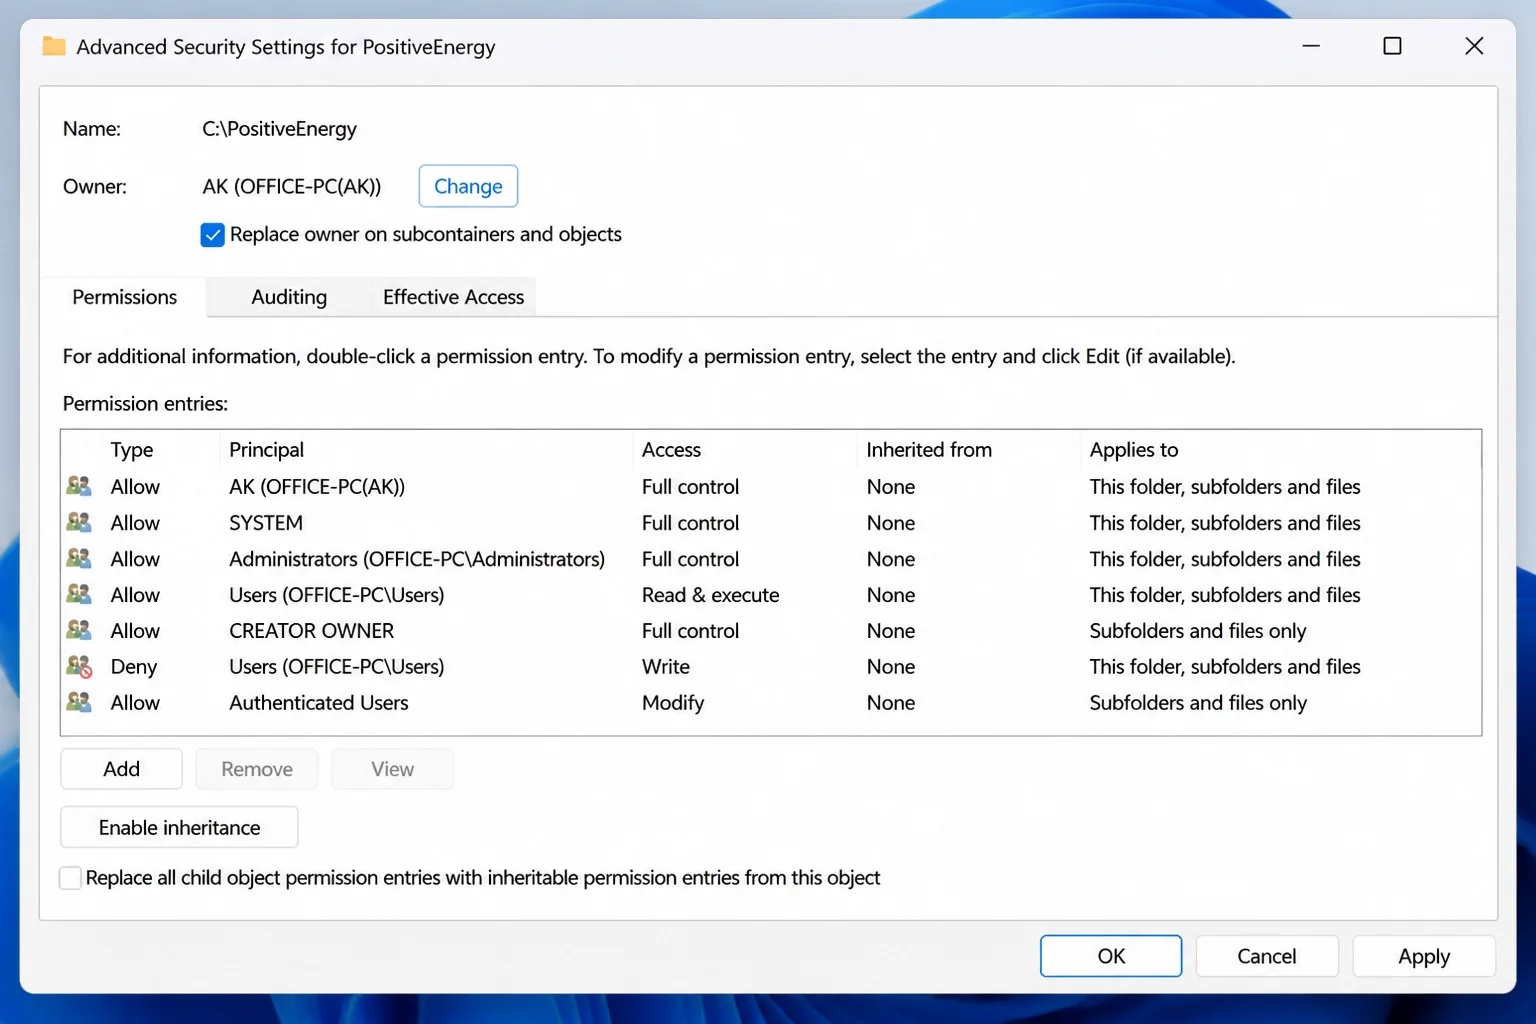
- Close Properties and reopen it. The Security tab will now let you edit permissions freely.
After taking ownership, grant yourself Full Control under the permissions list so you can read, write, and manage the item going forward.
How to Check Effective Access
Effective Access shows the combined, real-world result of all permission entries for a specific account. It’s the fastest way to confirm whether a Deny entry is actually blocking someone. No guesswork.
- Right-click the file or folder, open Properties, then the Security tab.
- Click Advanced, then select the Effective Access tab.
- Click Select a user, type the username, click Check Names, then OK.
- Click View effective access.
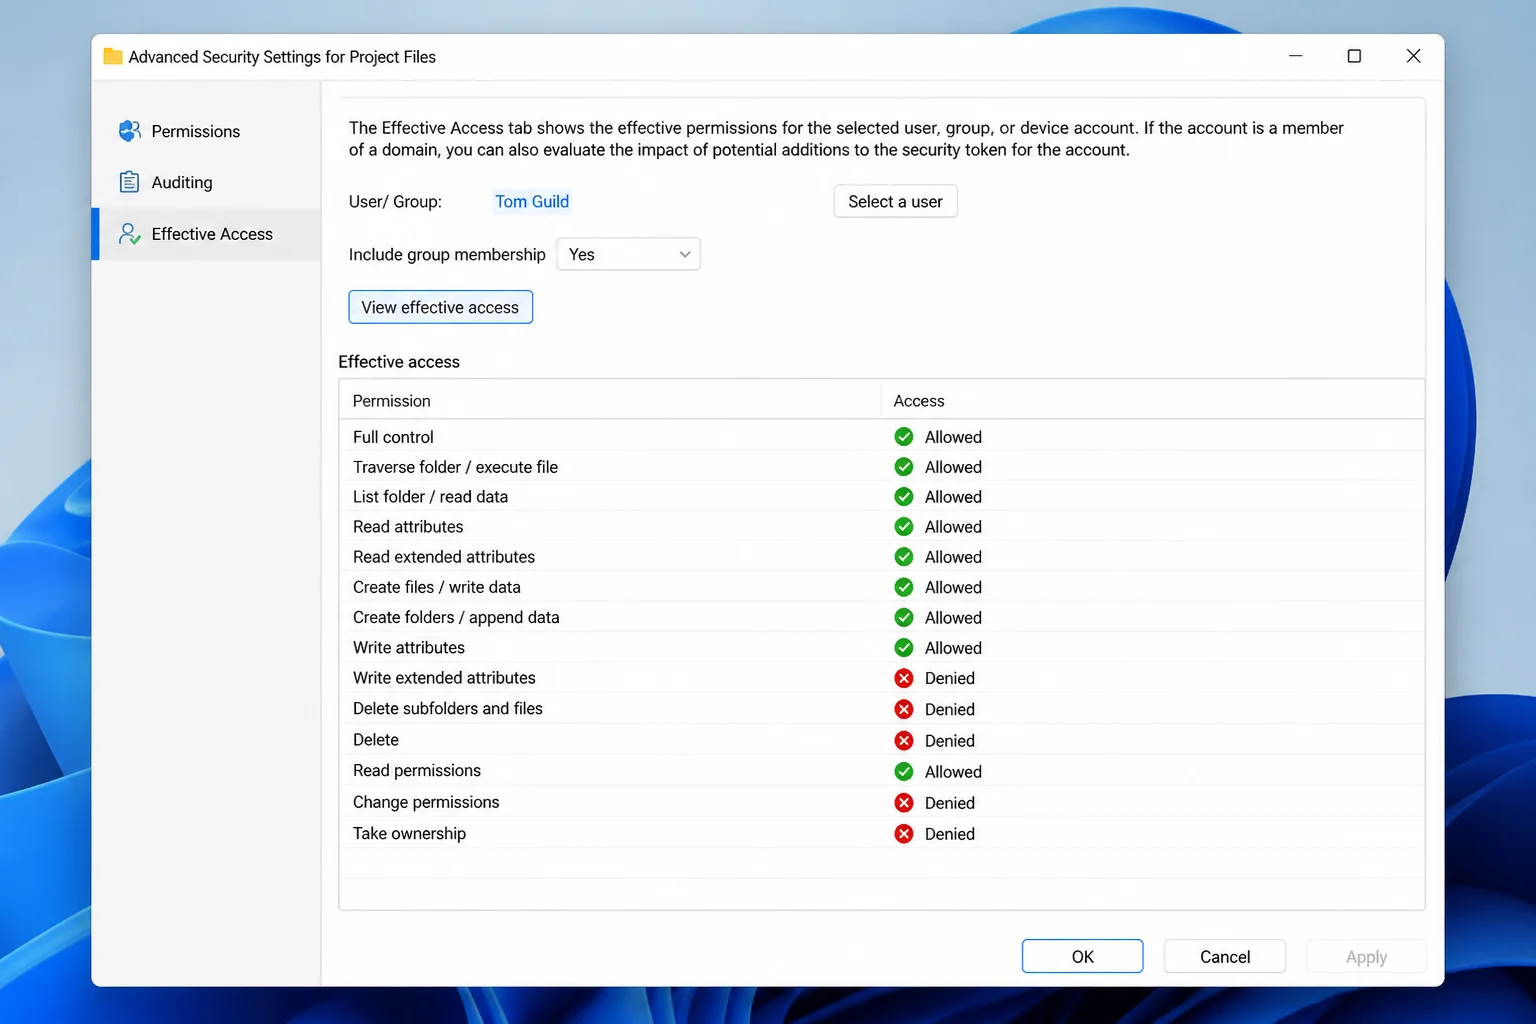
Green checkmarks mean the user has that right. A red X means they don’t, regardless of what individual Allow entries say. If you have conflicting permissions and aren’t sure which one wins, this tab resolves it definitively.
Common Permission Problems
“Access is denied” when opening a file or folder The file is owned by a different account. Take ownership using the steps above, then grant yourself Full Control.
The Security tab is missing or greyed out Your account doesn’t have administrative rights, or a device policy is hiding the tab. Right-click File Explorer and choose Run as administrator. On a managed device, check with your IT administrator.
Permissions keep reverting after you save Stuck in a loop where your changes disappear? Inheritance from a parent folder is almost certainly the reason. Disable inheritance on the item you’re configuring, and the changes will finally stick. On domain-joined PCs, Group Policy can also reset permissions on a schedule. That’s a fix your IT team needs to handle.
Account names look strange (user@domain.com or MicrosoftAccount\\user@example.com) Normal if you sign in with a Microsoft account or a work/school (Azure AD) account. Permissions work exactly the same way. Grant or deny access to that account just as you would a local user.
For Power Users: icacls
Editing permissions one folder at a time gets tedious when you have many to configure. icacls handles bulk changes from the command line. To grant a user Full Control over a folder and everything inside it:
icacls "C:\MyFolder" /grant Username:(OI)(CI)F /TRun Command Prompt as administrator.
Conclusion
For the typical case, blocking someone on a shared PC from a specific folder, the Security tab in Properties is all you need. If the checkboxes are greyed out, disable inheritance first. If everything is locked because of ownership, take ownership and then set your permissions.
Permissions reverting is the most confusing part, but inheritance explains it nearly every time. Disable it on the item directly, save your changes, and they’ll finally stay where you put them. Worth getting right the first time.